What this practice does
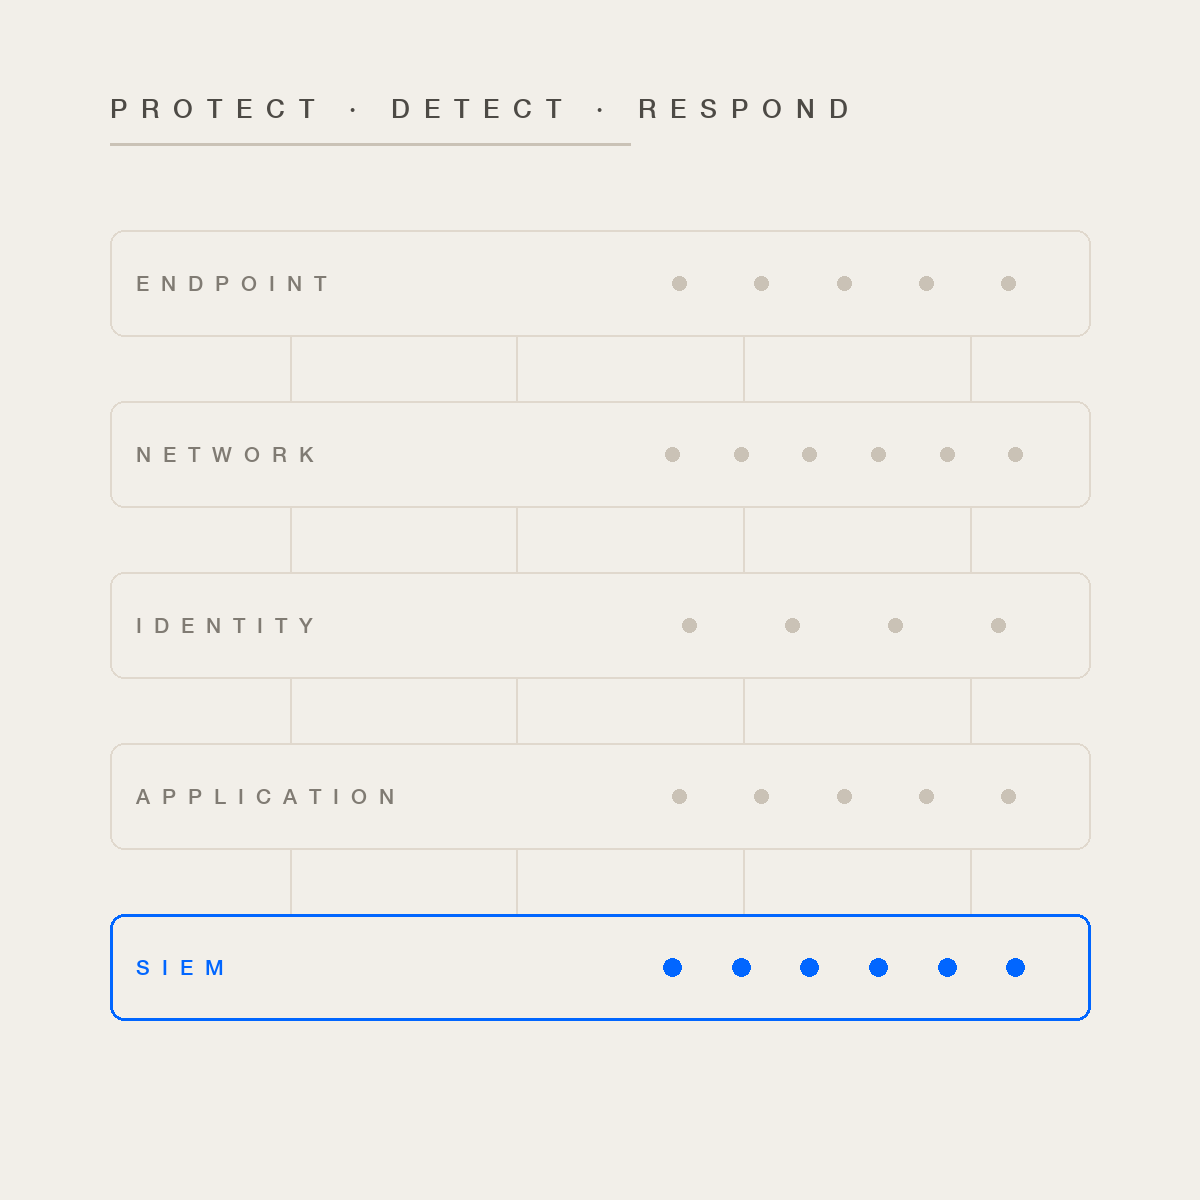
We secure the estate end to end — endpoints and data, the network, identity, applications, and the security operations that tie them together — combining our own engineering with proven platforms.
Where engagements usually start
- A regulatory finding or audit observation with a deadline attached
- Alerts arriving from a dozen tools with nobody able to see the whole picture
- Privileged access that was granted years ago and never reviewed
- Code shipping faster than security can review it
- A security estate assembled by procurement cycle rather than by design
What sets the team apart
Our people find critical vulnerabilities before attackers do. Team members have been credited in vendor halls of fame for zero-day discoveries and take part in bug bounty programmes, working with the affected organisations on remediation rather than stopping at disclosure. That offensive perspective informs how we build defences.
What we deliver
Endpoint & data security
- Endpoint detection and response
- Enterprise digital rights management and data classification
- Data loss prevention
- Database protection and audit
- File integrity and change management
Data privacy & governance
- Data discovery and classification
- Consent management and data subject rights automation
- Vendor risk management
- PDPL, GDPR and CCPA alignment across cloud, on-premises and hybrid estates
Network security
- Next-generation firewall and intrusion prevention
- Network access control across BYOD, IoT and OT
- Network detection and response, and user behaviour analytics
- DNS security, email and web gateway, and email fraud protection
- DDoS protection
Secure identity & authentication
- Identity and access management, with access certification and provisioning
- Privileged access management
- Multi-factor authentication and single sign-on
- Encryption, HSM and key management
- PKI and certificate lifecycle management
Application security
- Web application firewall
- Vulnerability management and secure code development
Security management
- SIEM — real-time analysis of alerts across the estate
- Configuration and vulnerability management
Technology we work with
Beyond the platforms we partner on directly, we deploy and operate a wider set of security technologies, chosen per estate rather than per vendor relationship — Trellix for endpoint and extended detection, Seclore for enterprise digital rights management, Securiti.ai for privacy and data governance, SailPoint for identity governance, Forescout for network access control, Darktrace for network detection and response, and Fortanix for encryption and key management. Where a client already owns a platform, we work with what is there rather than arguing for a replacement.
Regulatory alignment
Engagements are delivered against SAMA, NCA, NDMO and PDPL, with alignment to ISO 27001, PCI-DSS and SWIFT CSP where applicable. Compliance is designed into the controls rather than evidenced afterwards.
Global delivery — on-site, near-shore and offshore
Engineering capacity sits across four locations, so a programme can be staffed where it makes sense rather than where we happen to be. Most engagements use more than one.
- Riyadh, Saudi Arabia — head office. Client-facing delivery, architecture, and the engineers who work inside regulated environments.
- Dubai, UAE — regional office. Near-shore delivery across the GCC, on the same working week and time zone as Kingdom teams.
- London, United Kingdom — presence for clients and partners operating across UK and European markets.
- Chennai and Hyderabad, India — offshore engineering centres, where sustained build and run capacity scales.
Near-shore from Dubai keeps delivery inside the same business hours as the Kingdom, which matters when a release window or an incident needs a decision the same day. Offshore from Chennai and Hyderabad carries the volume work — development, testing, migration and ongoing support — at a cost base that makes long-running programmes sustainable.
Capacity is deliberately elastic. A build phase needs more engineers than the run phase that follows it, so teams scale up and down against the shape of the programme rather than a fixed contract, and specialists are drawn from the wider practices when a problem calls for them.